bikini/exploitarium: Exploitarium: Public Archive of Exploit
A curated archive of public exploit PoCs and vulnerability research writeups.
★ 4.0 / 5 iKeep scoreScreenshots
Quick facts
Overview
Exploitarium is a GitHub repository that serves as a consolidated archive of public proof-of-concept exploits and vulnerability research writeups. It includes various standalone PoC repos and new research entries, often with AI-assisted fuzzing workflows.
Getting started with GitHub - bikini/exploitarium: A single archive of public exploit PoCs and vulnerability research writeups. At the time I post these, none have been reported. Feel free to report them yourself and take credit for the CVE if handed out lulz. Please do not abuse these. I do this so to allure people into the field, and I’ve always found this is the most efficient way
- Clone the repositoryClone the Exploitarium GitHub repository to your local machine using 'git clone https://github.com/bikini/exploitarium'.
- Navigate to research entryBrowse the repository to find a specific exploit or vulnerability research entry of interest.
- Review READMECheck the README or documentation within the relevant folder for setup instructions and usage details.
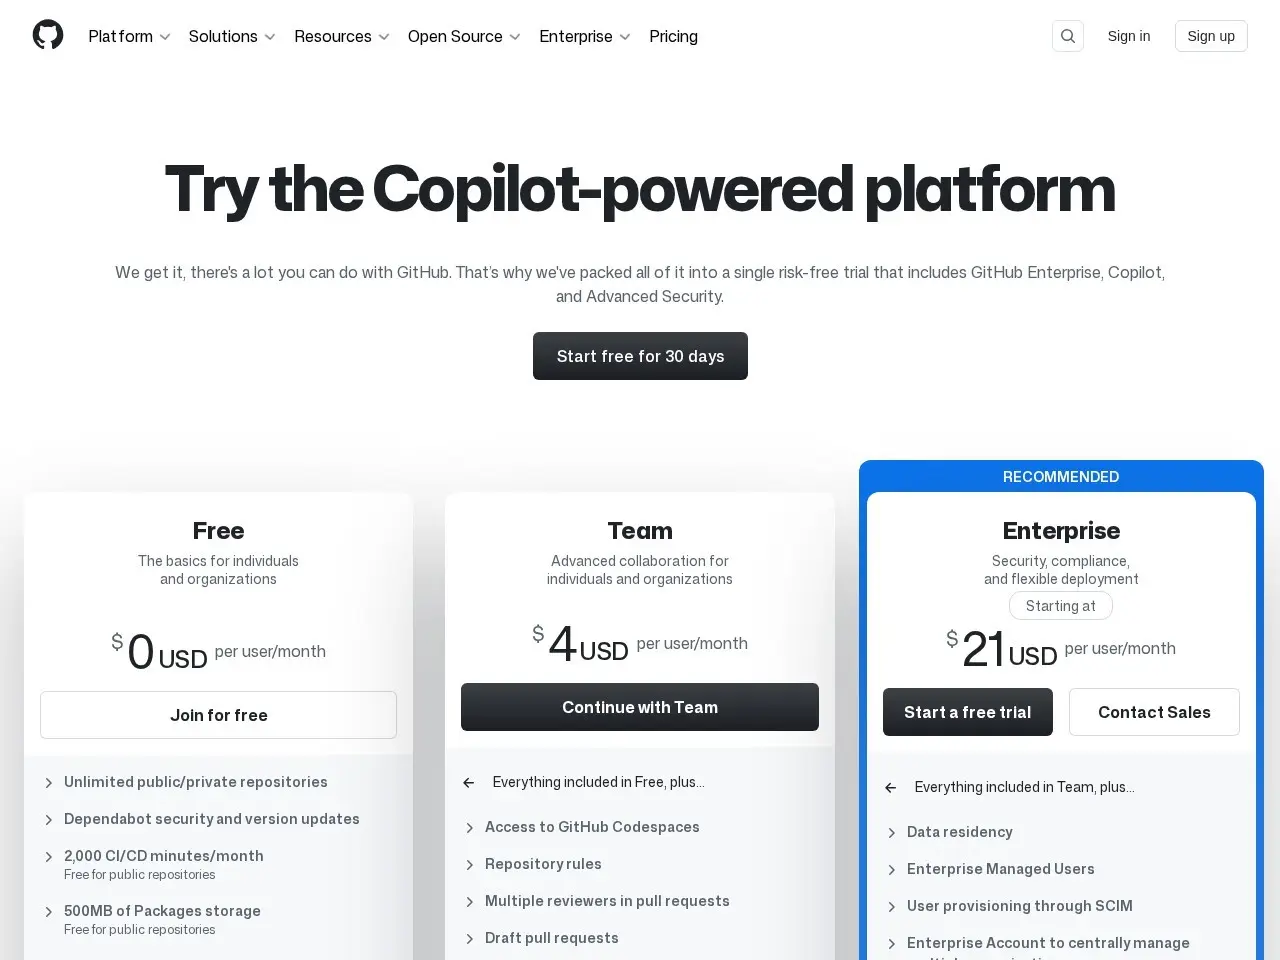
- Set up environmentPrepare the necessary environment or dependencies as specified in the research entry's documentation.
- Run PoCExecute the provided proof-of-concept exploit or follow the research workflow as documented.
Pricing
| Plan | Price | Note |
|---|---|---|
| Open-source | Free | Publicly available on GitHub |
💡 Indicative pricing — check the official rates at github.com · Updated 7/16/2026
Original pricing screenshotKey features
- Archive of public exploit PoCs
- Vulnerability research writeups
- AI-assisted fuzzing workflows
- Self-contained folders for each research entry
- Original README and tracked files preserved
- Regular updates with new PoCs
Pros
- Comprehensive collection of exploit PoCs
- Useful for security researchers and bug bounty hunters
- Clear documentation and AI-assisted formatting
Cons
- Potential ethical concerns regarding misuse
- Some PoCs may require adjustments for different environments
Use cases
- Security researchers analyzing vulnerabilities
- Bug bounty hunters looking for exploit references
- Developers learning about fuzzing and exploit development
The verdict
Exploitarium is a valuable resource for security researchers and bug bounty hunters, offering a well-documented archive of exploit PoCs and vulnerability research. However, users should exercise caution to avoid misuse.
✓ Who should use it
Security researchers and bug bounty hunters who need reference material for exploit development and vulnerability analysis.
✕ Who should skip it
Those without a background in cybersecurity or ethical hacking, as the content may be too technical or ethically sensitive.
Categories
Community
- Discord ↗Join for research, help, documentation, and more useful information.
Great for
Featured in
Frequently asked questions
Is GitHub - bikini/exploitarium: A single archive of public exploit PoCs and vulnerability research writeups. At the time I post these, none have been reported. Feel free to report them yourself and take credit for the CVE if handed out lulz. Please do not abuse these. I do this so to allure people into the field, and I’ve always found this is the most efficient way free?
GitHub - bikini/exploitarium: A single archive of public exploit PoCs and vulnerability research writeups. At the time I post these, none have been reported. Feel free to report them yourself and take credit for the CVE if handed out lulz. Please do not abuse these. I do this so to allure people into the field, and I’ve always found this is the most efficient way is free to use.
What is GitHub - bikini/exploitarium: A single archive of public exploit PoCs and vulnerability research writeups. At the time I post these, none have been reported. Feel free to report them yourself and take credit for the CVE if handed out lulz. Please do not abuse these. I do this so to allure people into the field, and I’ve always found this is the most efficient way best for?
Security researchers and bug bounty hunters looking for exploit references and vulnerability research.
Does GitHub - bikini/exploitarium: A single archive of public exploit PoCs and vulnerability research writeups. At the time I post these, none have been reported. Feel free to report them yourself and take credit for the CVE if handed out lulz. Please do not abuse these. I do this so to allure people into the field, and I’ve always found this is the most efficient way have an API?
No, GitHub - bikini/exploitarium: A single archive of public exploit PoCs and vulnerability research writeups. At the time I post these, none have been reported. Feel free to report them yourself and take credit for the CVE if handed out lulz. Please do not abuse these. I do this so to allure people into the field, and I’ve always found this is the most efficient way does not offer a public API.
Can I self-host GitHub - bikini/exploitarium: A single archive of public exploit PoCs and vulnerability research writeups. At the time I post these, none have been reported. Feel free to report them yourself and take credit for the CVE if handed out lulz. Please do not abuse these. I do this so to allure people into the field, and I’ve always found this is the most efficient way?
Yes, GitHub - bikini/exploitarium: A single archive of public exploit PoCs and vulnerability research writeups. At the time I post these, none have been reported. Feel free to report them yourself and take credit for the CVE if handed out lulz. Please do not abuse these. I do this so to allure people into the field, and I’ve always found this is the most efficient way can be self-hosted.
Who should use GitHub - bikini/exploitarium: A single archive of public exploit PoCs and vulnerability research writeups. At the time I post these, none have been reported. Feel free to report them yourself and take credit for the CVE if handed out lulz. Please do not abuse these. I do this so to allure people into the field, and I’ve always found this is the most efficient way?
Security researchers and bug bounty hunters who need reference material for exploit development and vulnerability analysis.
Reviews 4.0 ★ · 1 review
Exploitarium stands out as a meticulously curated archive of exploit PoCs and vulnerability research, making it a goldmine for security professionals. The use of AI-assisted fuzzing workflows adds a modern twist to traditional research methods, though the ethical implications of such a public repository are worth considering. For those in the cybersecurity field, this resource offers invaluable insights and references, but it's best suited for experienced researchers who can navigate its content responsibly.
No reviews yet. Be the first to review GitHub - bikini/exploitarium: A single archive of public exploit PoCs and vulnerability research writeups. At the time I post these, none have been reported. Feel free to report them yourself and take credit for the CVE if handed out lulz. Please do not abuse these. I do this so to allure people into the field, and I’ve always found this is the most efficient way.
Write a review
Related tools